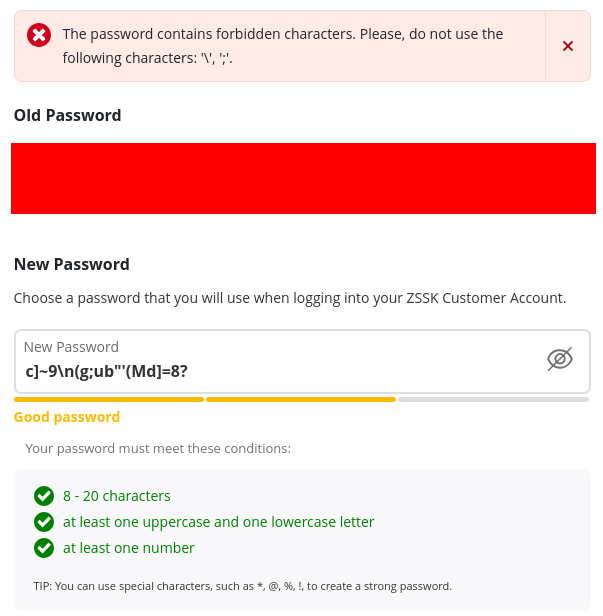
https://konto.zssk.sk/zk/new#step1
Also, it only seems to show “Strong password” if any of these characters is used: !@, and not other special characters.
I just don’t get this. Is it lazy programming? I don’t really program anymore and was never much if one, but I though at least some languages ad a concept of taking an input literally allowing special characters without injection or something. Forget what it’s called…
The fact its specifically "" and “;” makes it seem really likely they’re worried about SQL injections, meaning they must be using a super insecure SQL library and also sticking the password directly in the SQL query (so definitely no hashing)
AKA, here are the characters you can use to do a form injection on our website.
That and maximum character limits of 12-20 are insane to me
How large is the file a password is stored on? Can’t be more than a few kB. You could probably store the plaintext passwords of literally every Facebook account on one reasonably sized hard disk. There’s no reason we couldn’t use 500-character passwords if we wanted. A handful of my passwords are over 1,000 characters.
I’d reckon extreme length is much more effective for security than special characters. I’d reckon
1TimewhenIwasatBandCamp,Istuckafluteinmyflutecaseis significantly more secure than any password 8 characters in length for any aspiring flautist.
If the password is hashed (it should), it’d always be the same length, and original’s length would only impact how long hashing would take
Exactly that’s why these limits are so stupid. Companies that limit passwords to only a few characters almost certainly have bad security practices.
When they don’t allow certain characters in the password, it makes you wonder if they are not hashing the passwords.
it’s worse. they’re not even using query binding, they’re just sticking the password into sql. a bound query would escape these characters properly, a raw query will just accept them as-is. they have a couple steps before they even get to hashing.
What’s worse is when they allow the backslash but you have to escape the backslash when you actually enter your password to log in.
They’re probably also not escaping/sanitizing input at all which is also super concerning.
Wonder if the username Bobby Tables is taken.
Here to say sanitize your inputs Bobby, but you got it covered fam. Cheers.
My bank doesn’t support any special characters in the password, and letters are case-insensitive. At least the limit is 30 characters, so that’s still good enough. Though I really wonder what kind of system doesn’t differentiate uppercase and lowercase letters.
Yet, somehow, they did implement OpenPGP for e-mail signing and encryption.
Most MySQL/MariaDB collations are explicitly case insensitive (and optionally but very commonly blind to diacritics and accent marks). Your bank is obviously doing queries against a plain text database column.
Little Bobby Drop Tables has a difficult life.