
1·
10 天前Pretty sure it’s entry. I think that the exit wound is on the other side.
Pretty sure it’s entry. I think that the exit wound is on the other side.

I’m not sure if this specifically is used, as it requires the browser to be already running. If not, the new browser instance is spawned as a child process to the malicious program, inheriting all of its restrictions.
In general, if you don’t have permission to do something yourself, it’s common to find someone who does and ask nicely (or maliciously) for them to do it on your behalf. This is called the confused deputy problem.
See also the security problems related to the setuid bit.
For example, sudo should be owned by root and have the setuid bit set. This means that every time you run sudo, it runs with the permissions of the root user. Now, sudo is typically strict about checking if you’re really allowed to run commands with elevated permissions, and only executes the command you give if it’s sure that ypu’re allowed to.
But, suppose that you could replace the call to the password cheking function with a call to exec. Now, your password is interpreted as a file path and the file it points to is run with the sudo process’ peemissions (root). Authentication has now been bypassed.
It was a made-up example, but I hope that it illustrates the point.
In the real world, buffer overflows can potentially write user-supplied data over something important, essentially giving you a chance of achieving something similar. (Incidentally, the Rust programming language practically eliminates this class of memory-related bugs.)
It will show up as coming from firefox. When you run the command with the browser already running, it tells the original browser process to open the tab, then exits. The restricted process never does any network I/O by itself.
and try to block it.
You would have to know in advance all the domains the malicious program would access and block them, so realistically, no, at least not pre-emptively.
I’m not really sure if it’s a problem on mobile, but even if network access is disabled for a process & its children, it may have access to processes that do have access.
As an example, open a firefox-based browser (not sure about chromium). Then, in a new terminal window, run the following command: firefox lemmy.ml, substituting firefox for the name of the open browser. Lemmy.ml should now be open in a new tab in the original browser window.
It doesn’t really matter if a program opens lemmy, but it can open any URL, like for example: https://example.com/data_vacuum/upload?user=ferric_carcinization&password=password123&pronouns=they-them&favorite-language=rust
A universal paperclip.
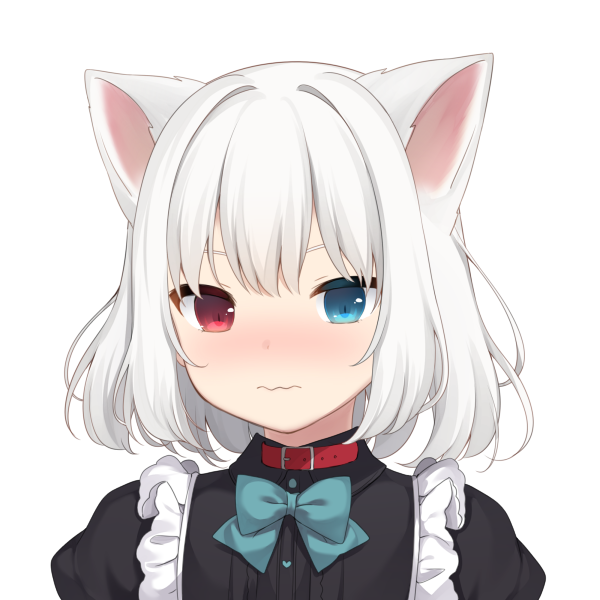
Translation:
Pen name: Ochinpo Tatsurou
Explanation:
Real name: Tatsuno Saori
Explanation:
Don’t take this the wrong way but you might be in the wrong instance.
How so? I’m not promoting any extreme viewpoints, and Lemmy.ml is the primary instance of Lemmy so surely ought to be welcoming
Unless it has changed recently, signing up requires copying a sentence from a communist text. This should hint at the views typically held here.
This is the instance run by Lemmy’s developers. And like them, a lot of the users here are communists, or at least other leftists.
I too hope that you won’t take this the wrong way, but you might feel more at home on another instance, with more like-minded individuals.

Please excuse my ignorance, but what is “the narwhal bacons at midnight”?
Which part was that? If you’re talking about the hallway in Sands of Karak, I’m pretty sure that it’s not required for progression.
Giggles in Gentoo.
Doesn’t Google require a phone number for account creation now?
It’s by no means new, but I’ve found OCR to be useful.
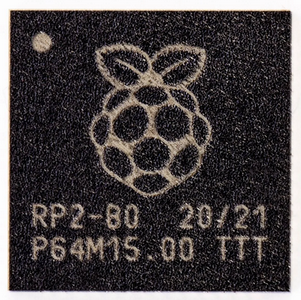
I’m also interested in RISC-V, but it feels weird that the cores are included in every single pico 2.
I guess that allows you to transition from ARM to RISC-V easier, but outside of hobby projects, I don’t see any reason to prefer the pico 2’s RISC-V cores over a RISC-V -only μC.
I just wish that they’d give a reason to use it over ARM. As I understand it, currently it’s in practice just a less effective version of the ARM cores without a FPU. For example, something like advertising a cool extension ARM doesn’t have, or making a RISC-V-only version for a bit cheaper.
This is about the pico 2, not the original, but would you know of a reason to use the RISC-V cores other than “Oh cool, it supports RISC-V now!”?
I’ve only used the ARM cores, and from what I remember from the documentation, the RISC-V cores didn’t beat ARM ones in anything. If I remember correctly the RISC-V cores also had a few limitations, like lacking FPUs.
Every single pico 2 build has two of both types of cores, so they have to have some use, right?
I could somewhat understand it if you could use more than two cores at once, but you can’t.
Where is this from? What was originally written on the sign?
Every autumn, a wave of red, orange, and gold sweeps south across the country. Here’s when fall colors will be their best across the United States in 2026.

To their credit, they do a bit more than just that. They also sync your personal information with their cloud, and often, the clouds of third parties as well.
Why do you assume that the ads cost the same?
I would assume that a piracy site might not be using Google’s ad platform. YouTube also has a lot of recognition as a popular & legitimate platform, which likely seems juicier to advertisers compared to a generic site. (Those advertising on a pirate site might not know that the ads are shown there)
YouTube also is not in a big need of extra revenue, unlike some other, smaller sites. And, depending on the site, they may or may not be able to show big, unskippable, profitable video ads before access downloads.
Please support small independent sites with ad-views. ;)

Peertube is probably the closest. I don’t really use either, but I’ve understood that peertube is a bit lacking in content.
As you’re here on lemmy.ml, I doubt it, but if you happen to be a “cryptocurrency enthusiast”, then odysee might also be an option, though I’m not sure hiw much of it is open-source.